State Bank of India (SBI) has confirmed a data-loss incident involving 3,897 customer records after personal information reportedly surfaced on the dark web. India’s largest public sector bank has yet to establish where the data originated, whether all the records are genuine or how many customers may be affected.
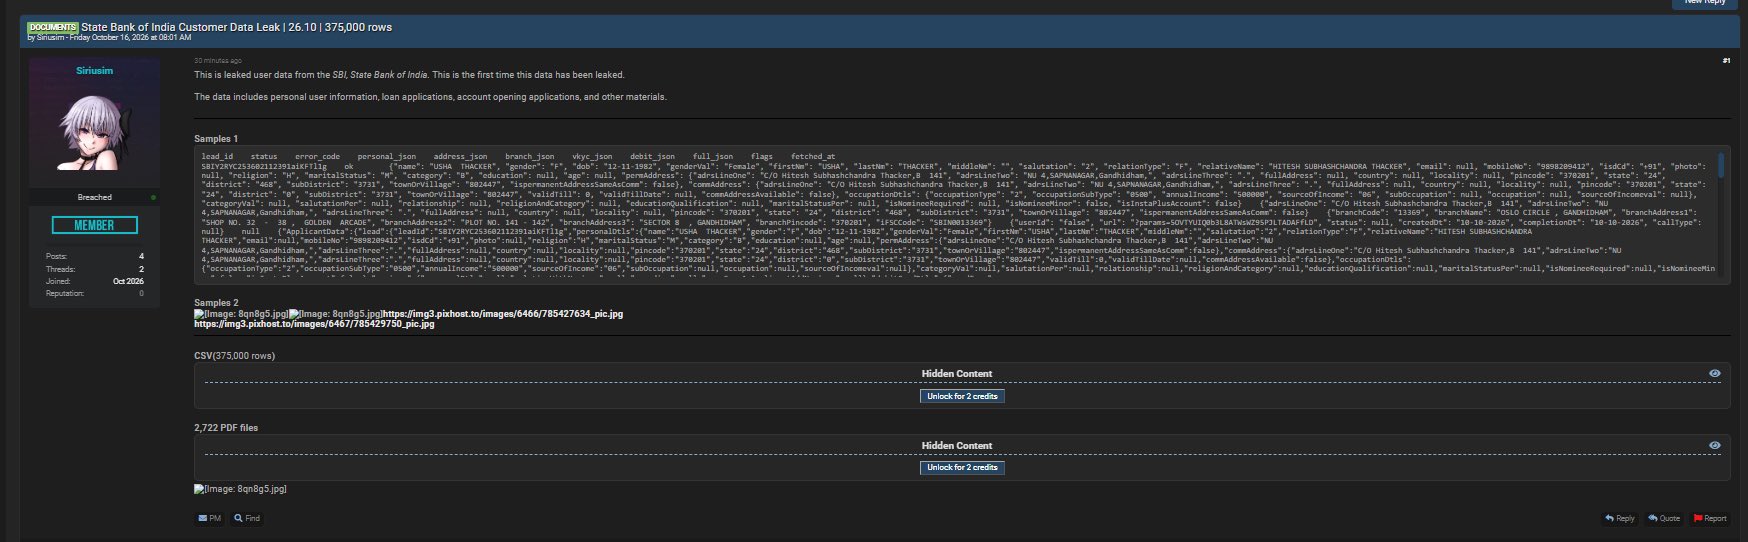
Here’s a screenshot of BreachForums listing.
In a stock-exchange filing dated October 21, SBI said the number of potentially affected records was preliminary. The bank has launched an investigation to determine the source and extent of the exposure.
The information reportedly includes names, registered mobile numbers, dates of birth, gender, email addresses, residential addresses, branch details, Customer Information File (CIF) identifiers, lead IDs and metadata associated with loan applications and related documents.
The filing does not list passwords, OTPs, card details, account balances, PAN numbers or Aadhaar numbers among the exposed data categories. However, the information could still help fraudsters impersonate bank employees and target customers with convincing phishing messages or fraudulent calls. A scammer who knows a customer’s personal details and loan-related information can make a fake request appear legitimate.
SBI identified the 3,897 records within a larger dataset of approximately 375,000 records reportedly available on the dark web. It has not clarified whether the records correspond to 3,897 unique customers or what the remaining dataset contains.
The bank said it received alerts on October 16 from its threat intelligence provider, the Indian Computer Emergency Response Team (CERT-In) and the Defence Cyber Agency under the Ministry of Defence. It activated its incident-response procedures and appointed an independent cybersecurity firm from CERT-In’s panel of approved security auditors to investigate the alleged compromise.
SBI said the incident has had no material impact on its core business operations, financial performance or business continuity. However, this does not establish whether individual customers face a risk of fraud. The bank has not disclosed whether it has notified affected customers.
The disclosure comes amid reports of a large dataset circulating on BreachForums, a cybercrime forum used to trade stolen information. On October 16, an account called CyberPulse56 posted on X that a threat actor using the name Siriusim had claimed to leak customer data associated with SBI.
The claim described approximately 375,000 rows in CSV format and 2,722 PDF documents, allegedly containing personal information, loan applications, supporting documents, account-opening forms and addresses.
The Free Press Journal examined the listing and reported that four sample records contained valid phone numbers. In one case, a WhatsApp profile picture matched the passport-size photograph included in a KYC document posted alongside the record. These checks suggest that the sample material may contain genuine personal information, but they do not confirm the authenticity of the entire dataset. SBI has not explicitly linked its investigation to the BreachForums listing, and the origin of the records remains unknown.
The information could have come from SBI’s systems, an associated entity or a third-party service provider involved in processing loan applications and customer documents. These are possibilities, not confirmed findings. The available evidence does not establish that SBI’s core banking systems were breached.
Understanding this is important because banking documents can pass through multiple systems during customer onboarding and loan processing. Identifying the source will help investigators determine whether the incident resulted from a breach of the bank’s infrastructure or a weakness elsewhere in the data-handling chain.
If you are an SBI customer, the immediate risk is targeted fraud. Scammers could use genuine names, addresses, phone numbers, and loan details to pose as bank employees, claim that an application needs attention or request sensitive information.
Customers should be cautious about unexpected calls and messages referencing their banking activity. Never share OTPs, passwords, or card credentials with callers, even if they know personal details. Suspicious activity can be reported to SBI through its official channels or to India’s national cybercrime helpline at 1930. SBI also lists report.phishing@sbi.co.in for reporting suspected phishing attempts.
Related Posts